Know your real exposure in minutes.
A program for teams that want to understand their Security Graph — how your apps, APIs, and cloud connect, and where attackers get in — measured against the OWASP Top 10 and Cloud Security Foundations. Connect read-only, and validated findings land in minutes.
- Read-only access, revoke any time
- Validated findings in minutes
- Every finding validated, zero scanner noise
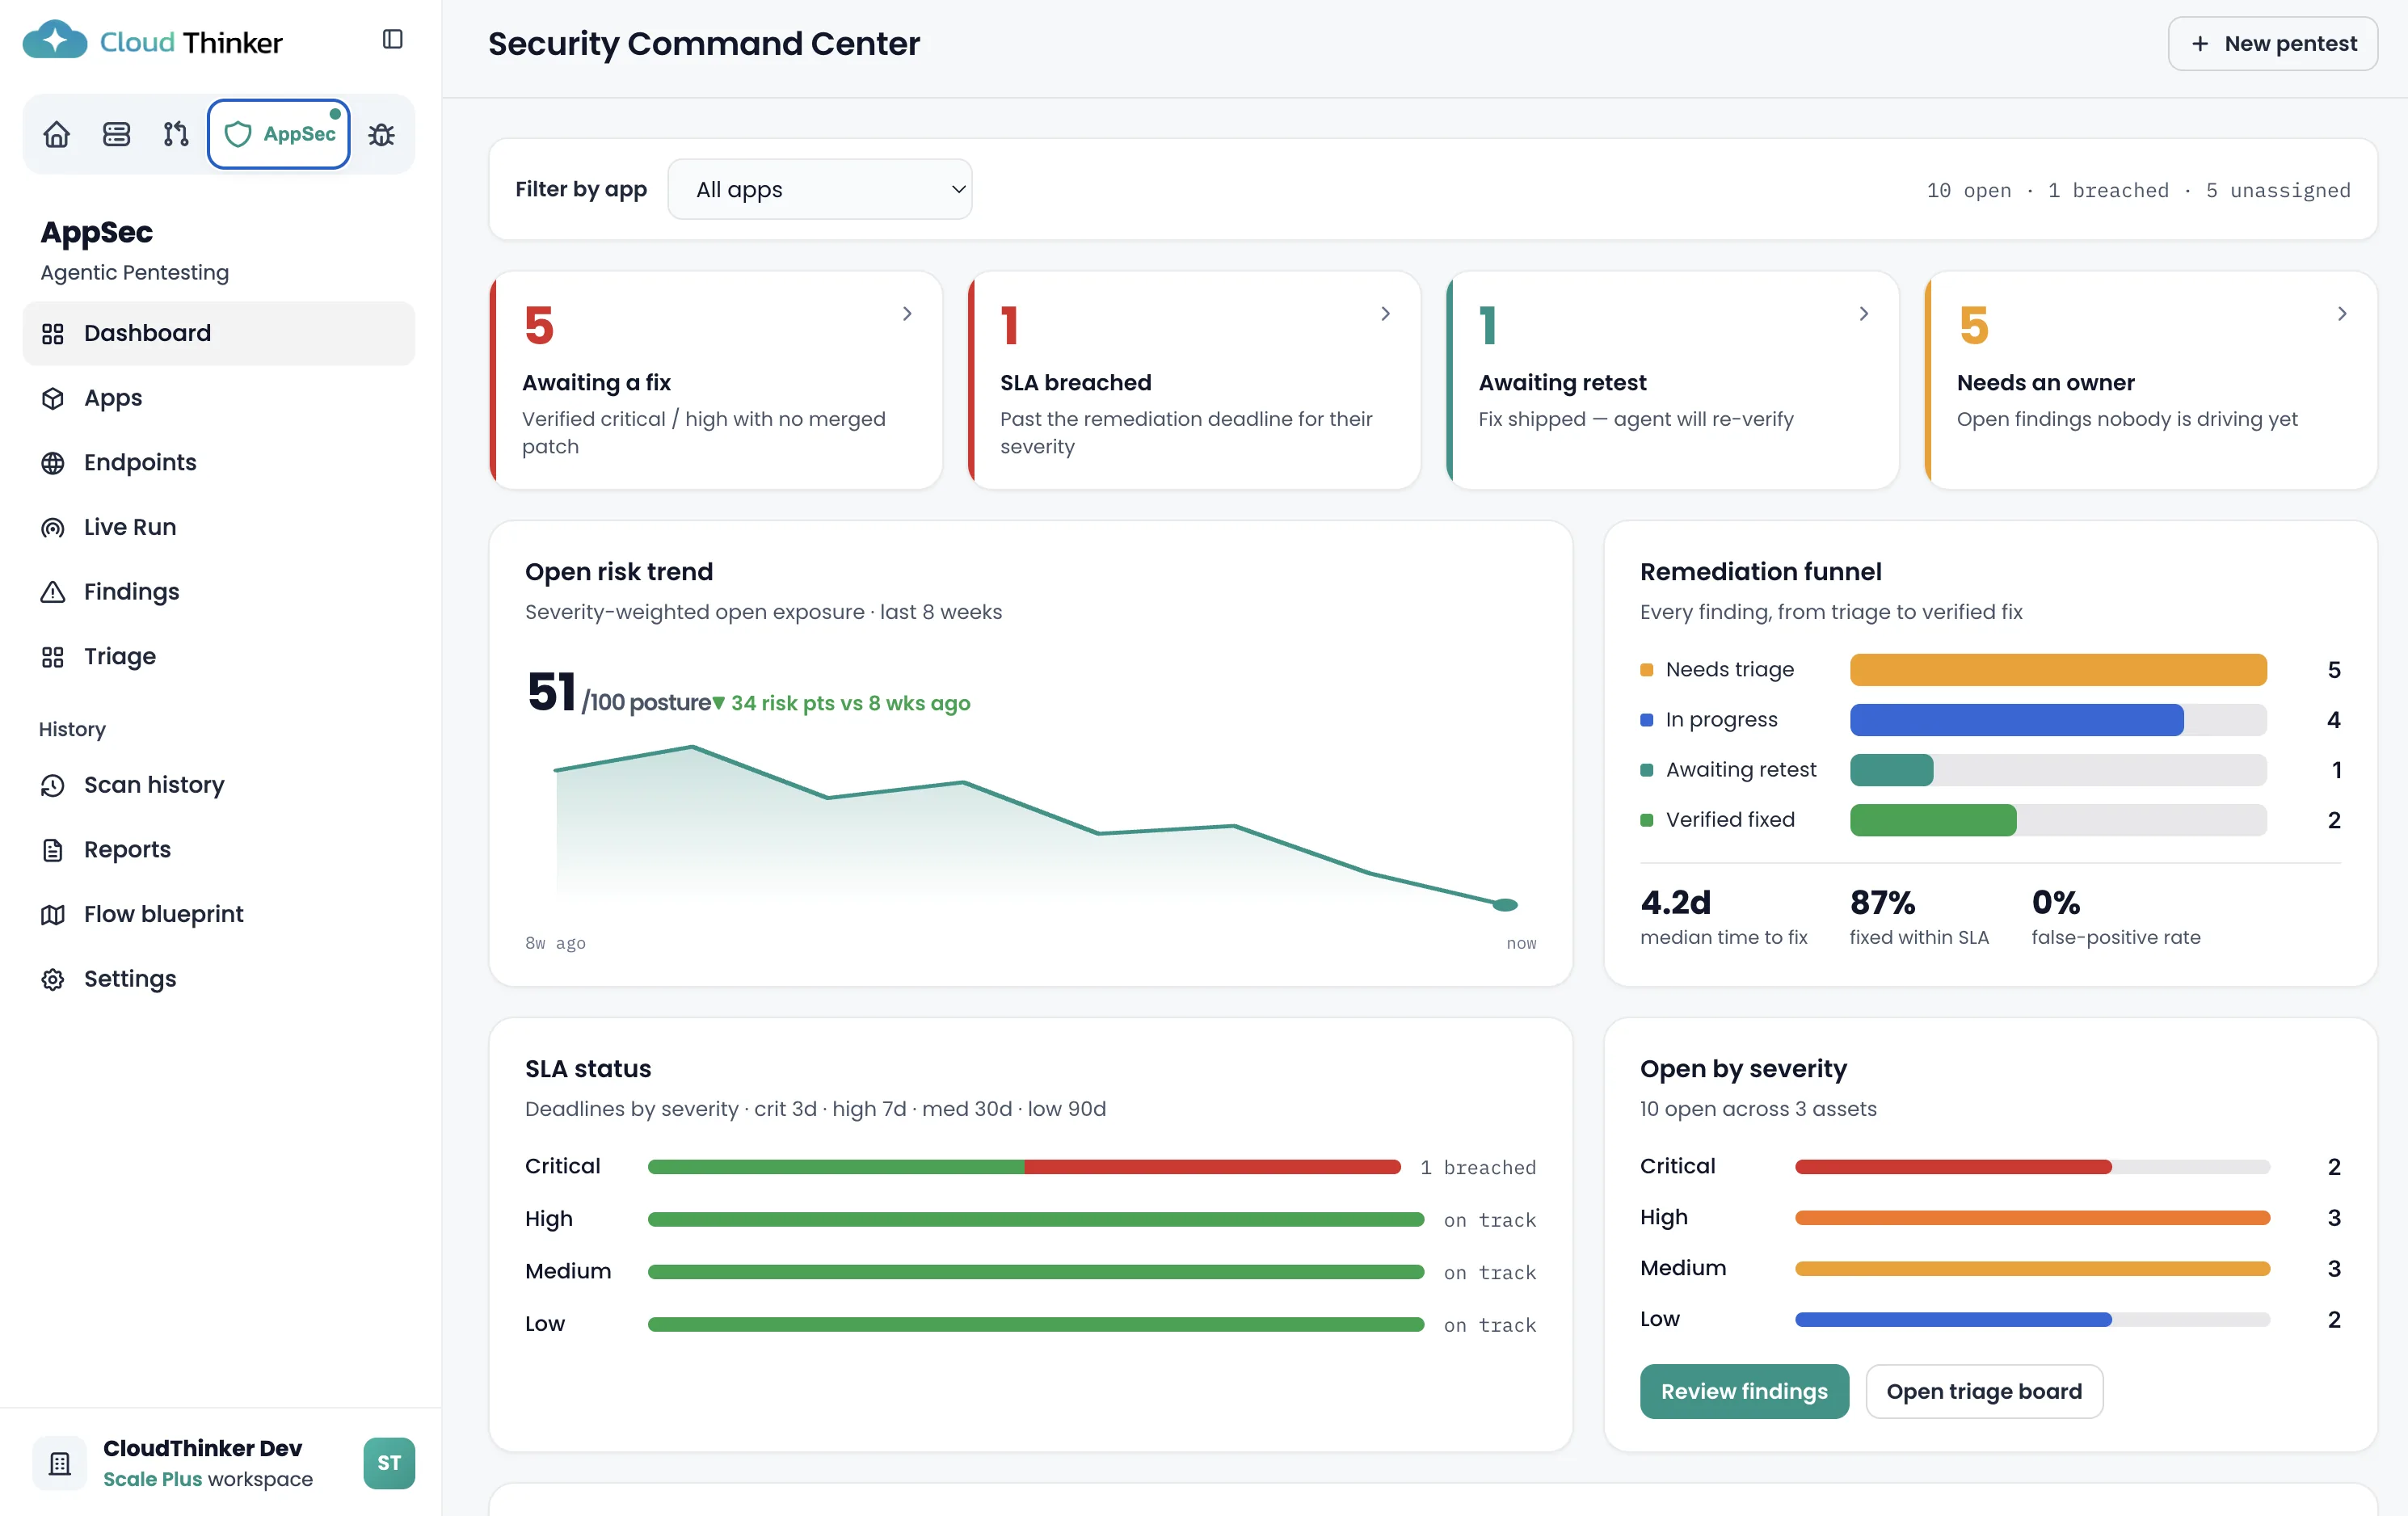
- CriticalBOLAValidated
- CriticalSQL injectionQueued
- HighSSRFQueued
What security teams say after connecting.
“The best thing is security — the things you do stay in your account: no data leak, no action without asking. As an expert, it understands problems clearly and makes proper decisions in minutes.”
Verified User in Financial Services
Enterprise, via G2
Rated on G2
Across verified customer reviews — security, cost, and incident response.
23%
Fewer incidents
With code and infrastructure review in the loop, reported by an enterprise customer on G2.
“It goes beyond identifying issues — the AI agents give actionable recommendations instead of just alerts.”
Verified User in IT & Services
Small-Business, via G2
“Streamlined cost management, issue identification, and incident reporting.”
Anh D.
CISO, via G2
Trusted by cloud teams and ecosystem partners






From connect to findings in minutes.
Connect
One read-only IAM role for your cloud, optional read access for your repos. No agents to install, nothing to deploy, scoped to the environments you approve.
Discover
Agents map everything an attacker can see: public and authenticated endpoints, your auth model, cloud resources, and dependencies — built from live discovery, not a questionnaire.
Validate
An agentic pentest proves which weaknesses are actually exploitable — safe, non-destructive checks with evidence attached. What cannot be proven does not make the report.
Readout
A 30-minute call with a security engineer: findings ranked by real risk, the top-3 fix plans, and one priced recommendation. The report is yours either way.
A report worth the meeting it starts.
Everything is yours to keep, whether or not you ever buy anything.
Attack-surface map
Every endpoint, service, and cloud resource an attacker can reach — including the ones nobody remembered were public.
Validated findings
Each finding proven with a safe exploit path, scored by severity, with the evidence attached. No maybes, no scanner noise.
OWASP API Top 10 coverage
The categories your auditor and your customers ask about — tested against your real application, not checklisted.
Top-3 fix plans
Concrete remediation for the three findings that matter most — scoped so your team can ship them this sprint.
Shareable report
A PDF and a shareable link — ready for your board, your auditor, or the enterprise customer asking for proof.
30-minute readout
A walk-through with a security engineer that ends with exactly one priced recommendation — never a sales sequence.
Built to pass your security review first.
Read-only, always
No write access is requested at any point in the assessment. You scope the environments, and you can revoke access the moment we are done.
Non-destructive validation
Exploit paths are proven with safe checks that never mutate data. Point us at staging, or run gray-box read-only against production.
SOC 2 Type II
CloudThinker is SOC 2 Type II audited, with deploy-anywhere options for regulated teams that cannot send data out.
Full audit trail
Every probe the agents run is logged in a tamper-evident trail — your security team can review exactly what was touched.
What security teams ask first.
- What access do you need?
- A read-only cloud role (one-click IAM setup) and, optionally, read access to your repositories. Everything is scoped to the environments you approve, and you can revoke it at any time.
- Is it safe to run against production?
- Yes. Validation is non-destructive — exploit paths are proven with safe read-only checks that never mutate data. Most teams point us at staging; gray-box read-only against production is equally supported.
- What does the assessment cost?
- For self-serve teams it is free. For enterprise engagements we charge a nominal assessment fee that is fully credited against your first program — it gives your security and procurement teams the contract vehicle they need to grant access.
- What happens after the readout?
- You get exactly one priced recommendation, based on what the assessment found. There is no obligation — the report, the fix plans, and the attack-surface map are yours to keep either way.
- How fast is it, really?
- Discovery starts the moment you connect, and your validated report is ready in minutes. Readout calls with a security engineer are capped each week — if the week is full, you get the next open slot.
Your attack surface won't wait.
Join free, connect read-only, and see your Security Graph with validated findings in minutes.
- Read-only access
- Findings in minutes
- No obligation