We root-cause one real incident for free.
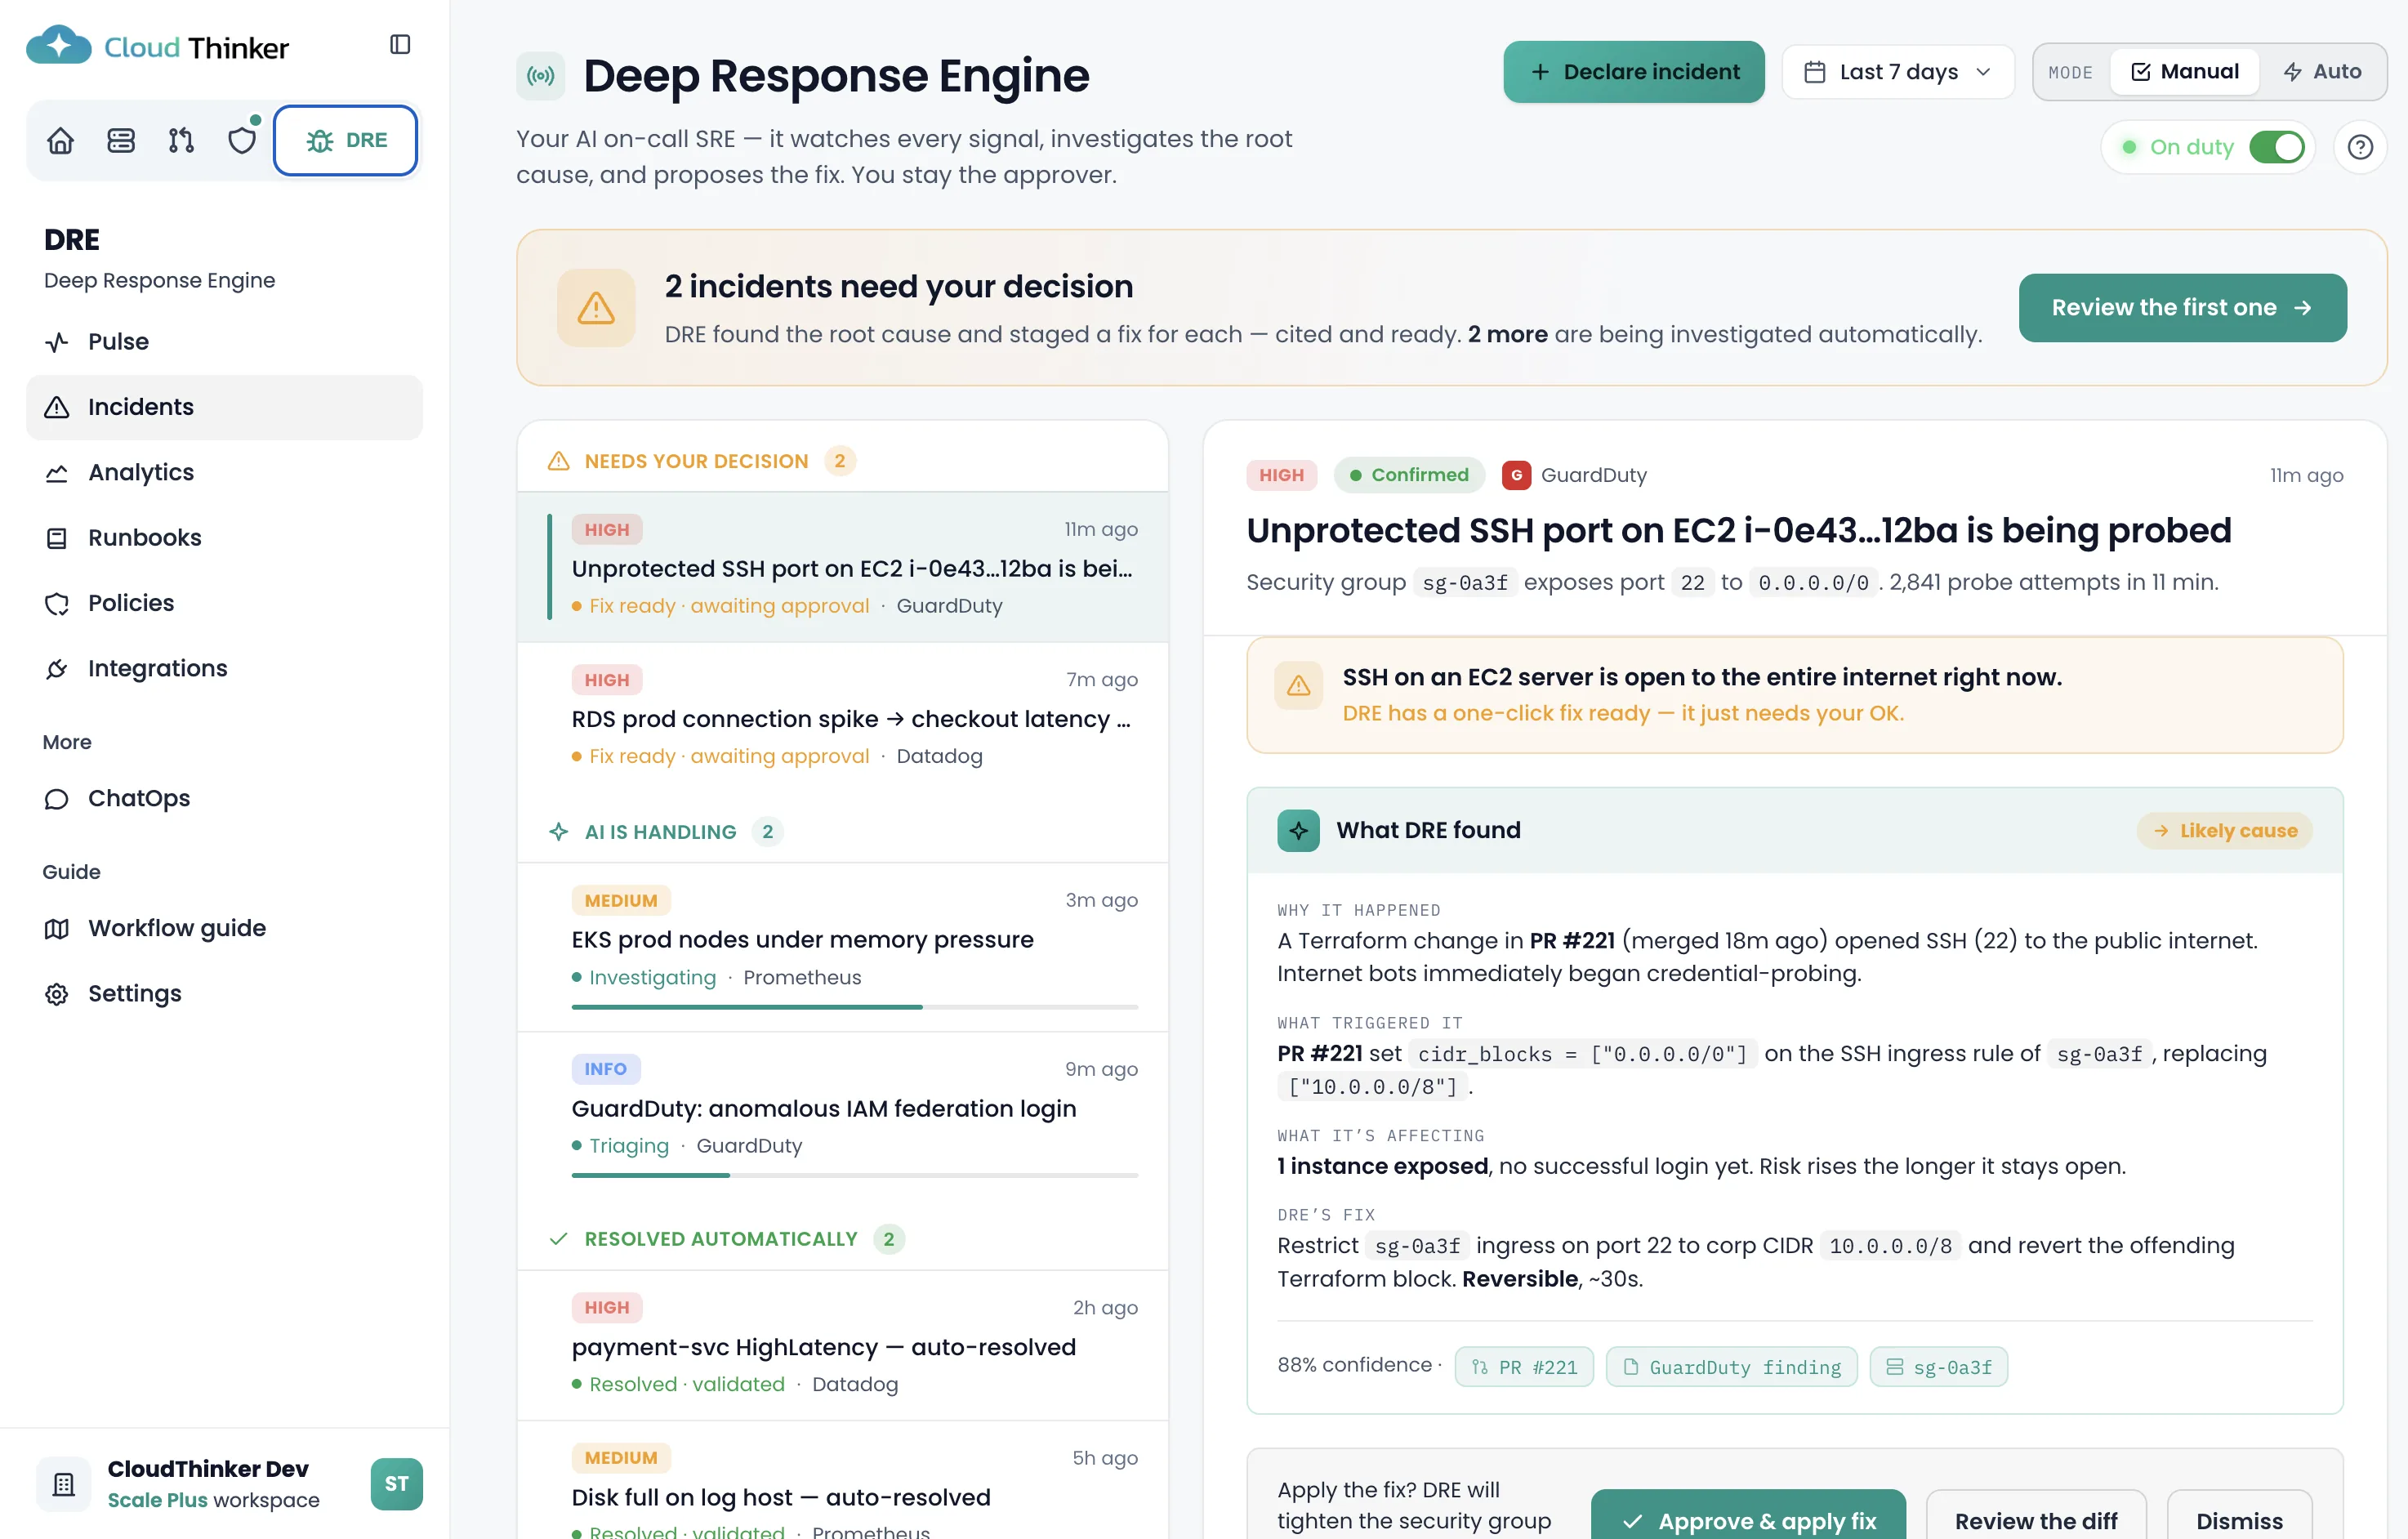
Nominate one production incident that still stings. Connect a read-only account, and Pulse correlates the signals across logs, metrics, traces, alerts, and code into a single root cause with a fix plan — delivered in minutes, not a war-room week. No obligation.
- Read-only access, revoke any time
- Root cause in minutes
- One incident, fully evidenced
- Detect5 signals
- AnalyzeQueued
- Root causeQueued
- Fix readyQueued
What teams say after their first incident.
“It goes beyond simply identifying issues — it helps resolve them with AI-powered automation. The AI agents provide actionable recommendations instead of just alerts, improving operational efficiency while reducing response times.”
Verified User in IT & Services
Small-Business, via G2
Rated on G2
Across verified customer reviews — incident response, cost, and security.
23%
Fewer incidents
With code and infrastructure review in the loop, reported by an enterprise customer on G2.
“Cuts out manual troubleshooting during outages by reading logs, pinpointing the root cause, and suggesting the exact fix.”
via G2
Trusted by cloud teams and ecosystem partners






From incident to root cause in minutes.
Nominate
Pick one production incident that still stings — the outage nobody fully explained, the p99 spike, the pager storm. One incident is all we need to prove it.
Connect
One read-only account across your observability and cloud. No agents to install, nothing to deploy, scoped to the sources you approve and revocable any time.
Investigate
Pulse clusters the signals across logs, metrics, traces, and alerts while agents find the root cause with evidence attached — a non-destructive read of what actually happened.
Readout
A 30-minute call: the root cause, a reversible fix plan, and one priced recommendation. The RCA is yours to keep either way.
An RCA worth the meeting it starts.
Everything is yours to keep, whether or not you ever buy anything.
Incident timeline
A minute-by-minute reconstruction of what happened, from the first anomaly to the page — so the story is finally settled.
Correlated signal cluster
The logs, metrics, traces, and alerts that belong to this incident, collapsed into one view instead of five tabs and a war room.
Root cause with evidence
The one thing that actually caused it, with the confidence score and the exact signals that prove it. No maybes, no guesswork.
Reversible fix plan
A concrete remediation your team can ship this sprint — scoped, sequenced, and reversible, so nobody is betting production on it.
Shareable RCA
A PDF and a shareable link — ready for your postmortem, your leadership, or the customer asking what went wrong.
30-minute readout
A walk-through with an engineer that ends with exactly one priced recommendation — never a sales sequence.
Built to pass your security review first.
Read-only, always
No write access is requested at any point in the investigation. You scope the sources, and you can revoke access the moment we are done.
Non-destructive investigation
Nothing is executed in production. Agents read and correlate your signals to find the root cause — they never run a command against your systems.
SOC 2 Type II
CloudThinker is SOC 2 Type II audited, with deploy-anywhere options for regulated teams that cannot send data out.
Full audit trail
Every read the agents perform is logged in a tamper-evident trail — your team can review exactly what was touched.
What teams ask first.
- What access do you need?
- Read-only access to your observability and cloud — logs, metrics, traces, and alerts, plus optional read access to the relevant repositories. Everything is scoped to the sources you approve, and you can revoke it at any time.
- Is it safe against production?
- Yes. The investigation is non-destructive — nothing is executed in production. Agents only read and correlate the signals you connect to reconstruct what happened; they never run a command against your systems.
- What does it cost?
- It is free — one incident, no obligation. For enterprise engagements a nominal fee may apply to grant access, and it is fully credited if you continue to the Resolve program.
- What happens after?
- You get the root cause, a reversible fix plan, and exactly one priced recommendation based on what we found. There is no obligation — the RCA is yours to keep either way.
- How fast is it, really?
- The investigation runs in minutes once you connect. Readout calls with an engineer are capped each week — if the week is full, you get the next open slot.
Your next incident is already forming.
Drop your email, nominate one incident, connect read-only, and get the root cause with a fix plan in minutes.
- Read-only access
- Root cause in minutes
- No obligation