


Free hands-on workshop
Run your SOC with AI agents.
A half day for security operations teams. Connect your SIEM and cloud read-only, then triage and contain real alerts with AI agents, guided by our engineers.
Half a day. Online or on-site. Free.
Half a day. Four blocks.
30 min
Foundations.
How AI agents triage alerts, and what they never do alone.
30 min
Connect.
Read-only access to your SIEM and cloud, set up live together.
90 min
Hands-on alerts.
Your analysts work real alerts with agents, from signal to containment.
60 min
Your playbook.
A containment policy, a first use case and a 30-day rollout.
Inside the workshop.
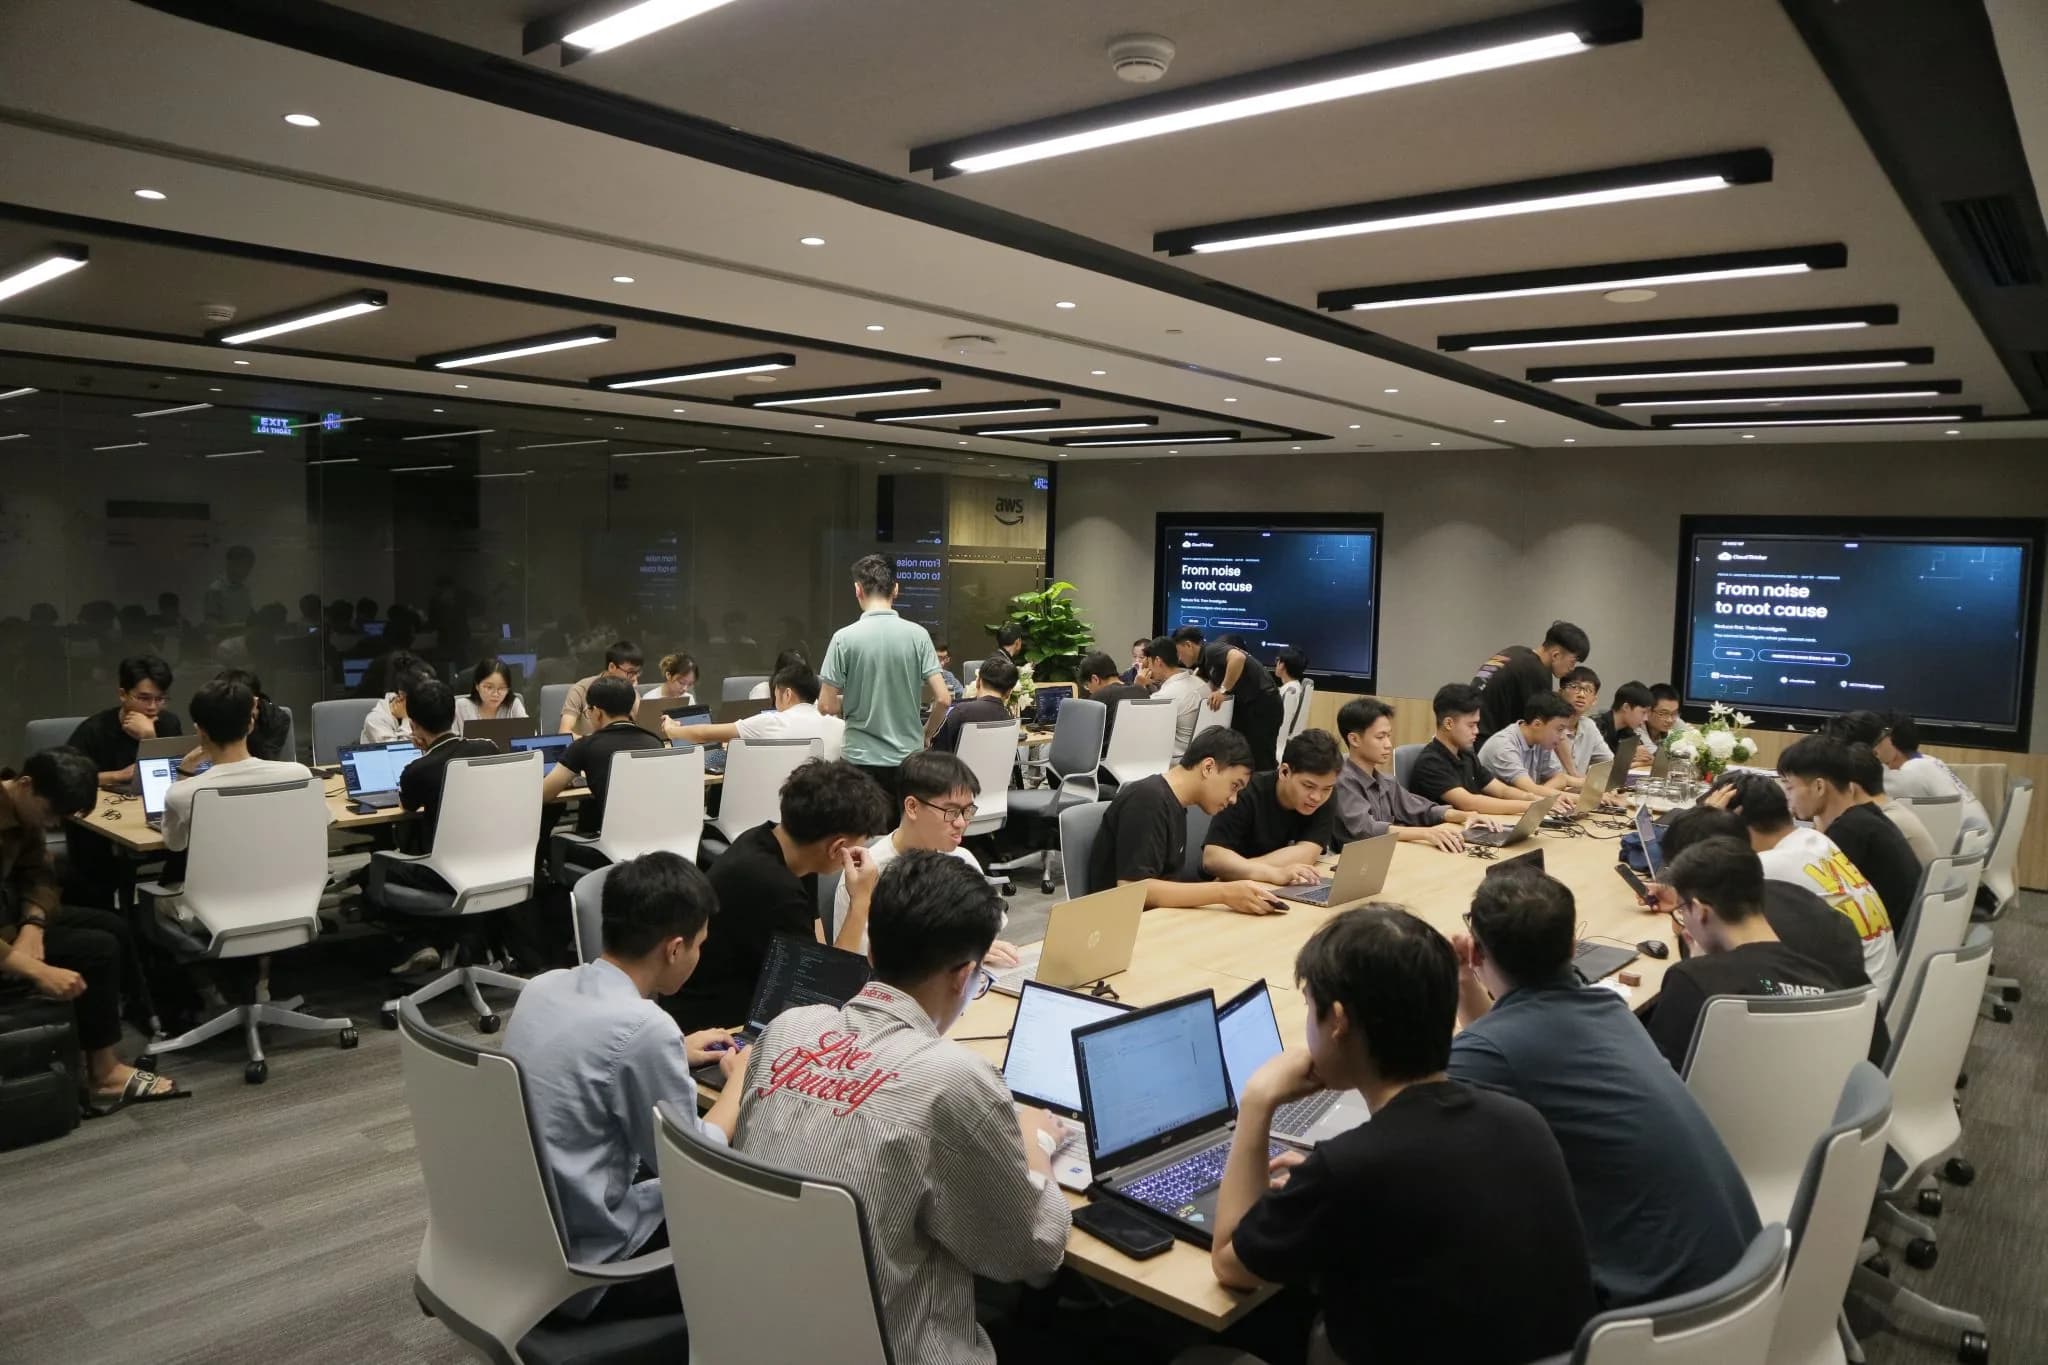
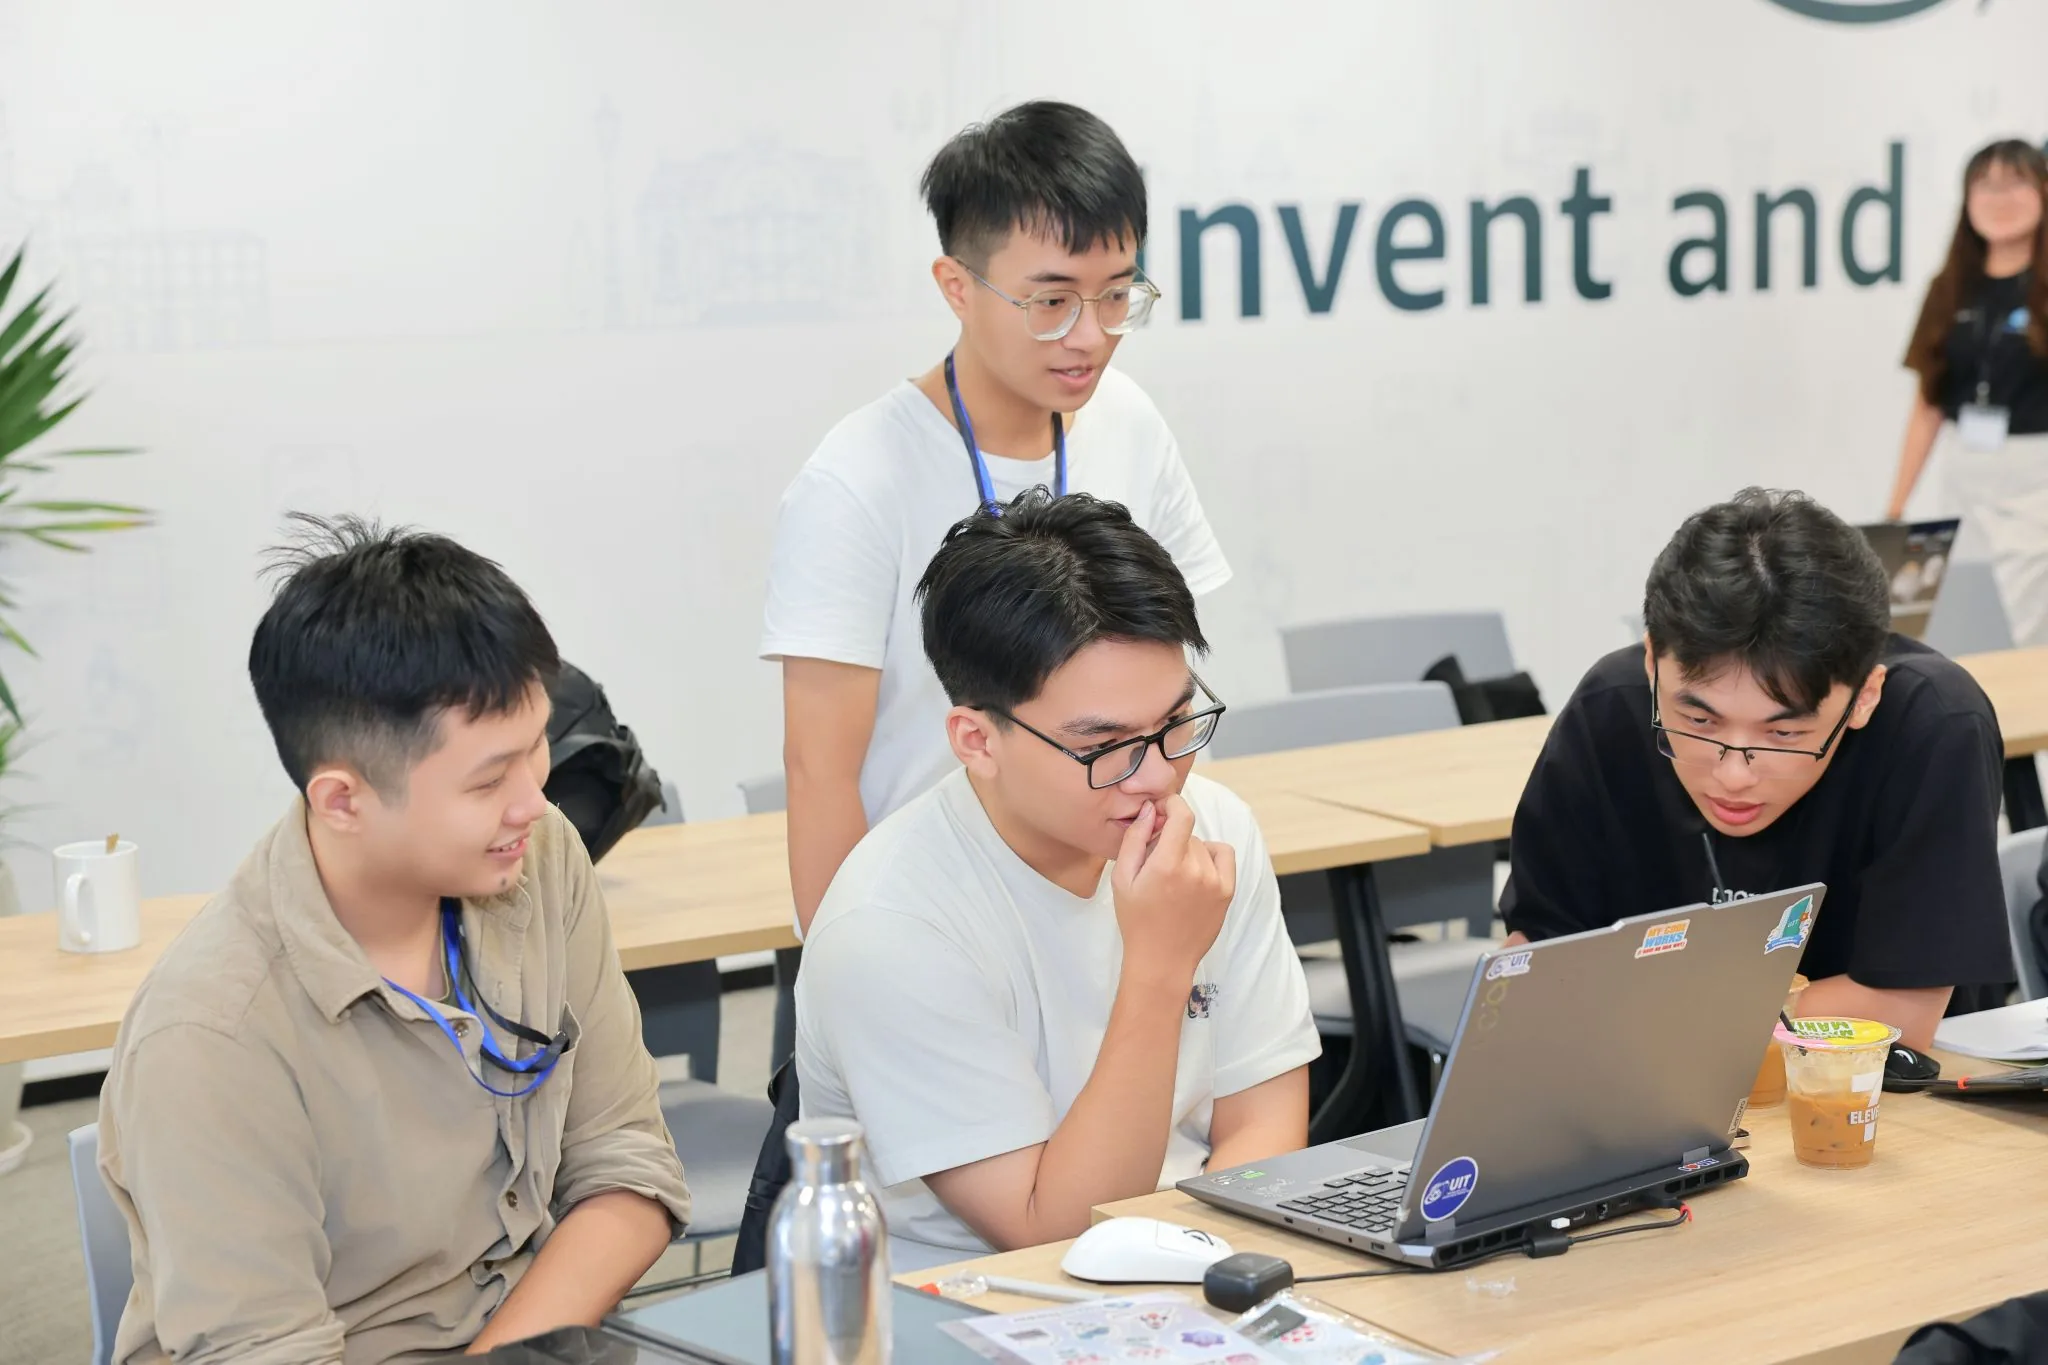
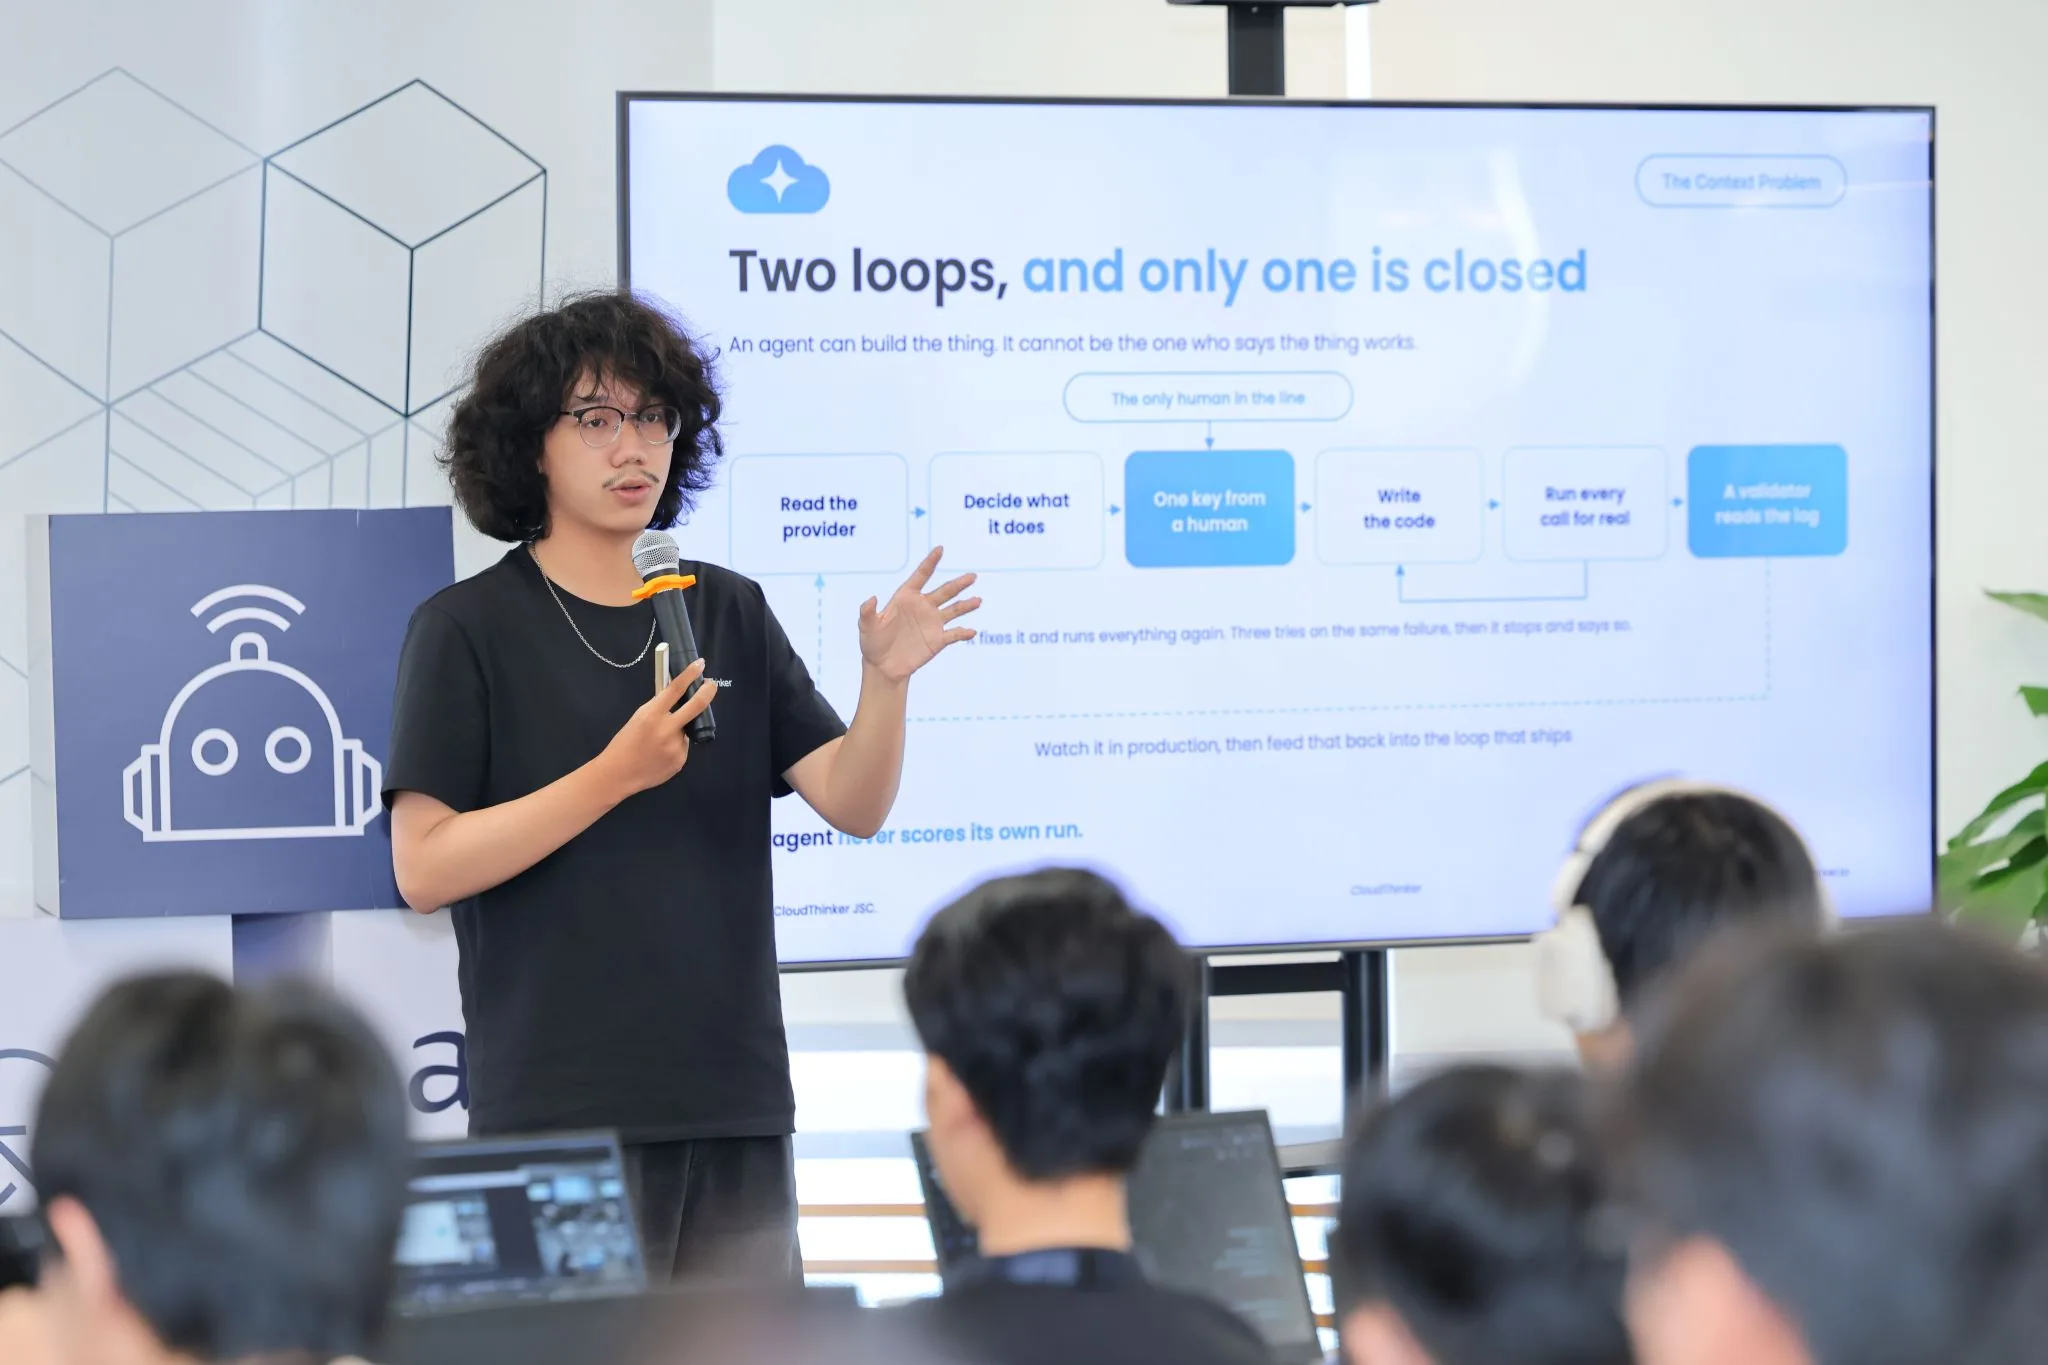
Built for the people on shift.
SOC analysts.
Who triage alerts all day.
Detection and response engineers.
Who write the rules and run the playbooks.
Security leaders.
Who decide how AI enters the SOC.
What your team takes home.
A working setup.
Read-only, on your SIEM and cloud, ready for the next alert.
Your triage baseline.
How long an alert takes today, and where it stalls.
A 30-day plan.
The first use case, the containment policy and who approves what.
Taught by the team behind the agents.
The engineers who build CloudThinker Cyber run every session. CloudThinker is SOC 2 Type II audited, and every agent action is logged with who approved it.
Investigating production issues for teams at



What security teams ask first.
Who should attend?
Two to eight people from your SOC, detection engineering or incident response, plus one security lead who can decide on next steps.
What do we need to prepare?
Read-only access to your SIEM and one cloud account, which takes about 15 minutes to set up. Not ready yet? We can run the session on our sandbox with sample alerts.
Is it really free?
Yes. There is no fee and no obligation. If you want to continue after the workshop, we will recommend one next step, and the 30-day plan is yours either way.
Online or on-site?
Either. We run it online for any time zone, or on-site with your team. We agree the format when we confirm your date.
Is our data safe?
Agents connect read-only to the systems you choose and never act outside your policy. You can revoke access at any time, and every action is logged.
Your next alert, with agents.
Free. Hands-on. Your own SOC.