The 10 Best AI SOC Platforms in 2026, Compared
Checked November 4, 2026. This was the year the money and the acquisitions arrived in the AI SOC market. Torq raised a $140M Series D in January. Exaforce raised $125M in May. In June, Cisco agreed to buy WideField Security to strengthen Splunk's agentic SOC. Cribl bought Radiant Security's AI SOC technology in August, and Palo Alto Networks bought Console in September. Meanwhile the big platforms shipped their own agents: Google's triage agent went generally available in June, and SentinelOne opened Purple AI investigations to every customer the same month.
Every product below investigates alerts. They differ on four things: what data the agent can reach, how it shows its verdict, who takes the action, and where it runs.
Disclosure: CloudThinker is our product, and it's on this list. Every other entry is described from the vendor's own website, docs and press releases as of the date above. We haven't run hands-on tests of the others. Every vendor roundup we read ranks its own product first, ours included, so every claim below links to the vendor's page and vendor numbers are labeled as vendor claims. Prices and features in this market change monthly, so check the live pages before you buy. The numbering isn't a ranking: CloudThinker comes first so the disclosure sits next to it, the standalone platforms follow, then the agents built into a larger platform.
How we chose and compared
A product made the list if AI agents investigate security alerts end to end and return a verdict, and if it's sold as a product you can buy today. Chat assistants that only answer an analyst's questions didn't qualify, and neither did managed detection services that use AI only behind the scenes. If you want the background first, read why AI-powered attacks need a different kind of SOC.
01Reach
What it sees
The SIEM, EDR, identity, cloud and email data the agent can query.
02Verdict
How it shows its work
The evidence, the reasoning, and what it says when it isn't sure.
03Response
Who presses the button
Recommendations only, gated actions, or autonomy you can dial up.
04Fit
Where it runs
An overlay on your stack, or an agent inside one vendor's platform.
We didn't rank on price, but where a vendor publishes one, it's in the entry. Most of this market still sells by quote.
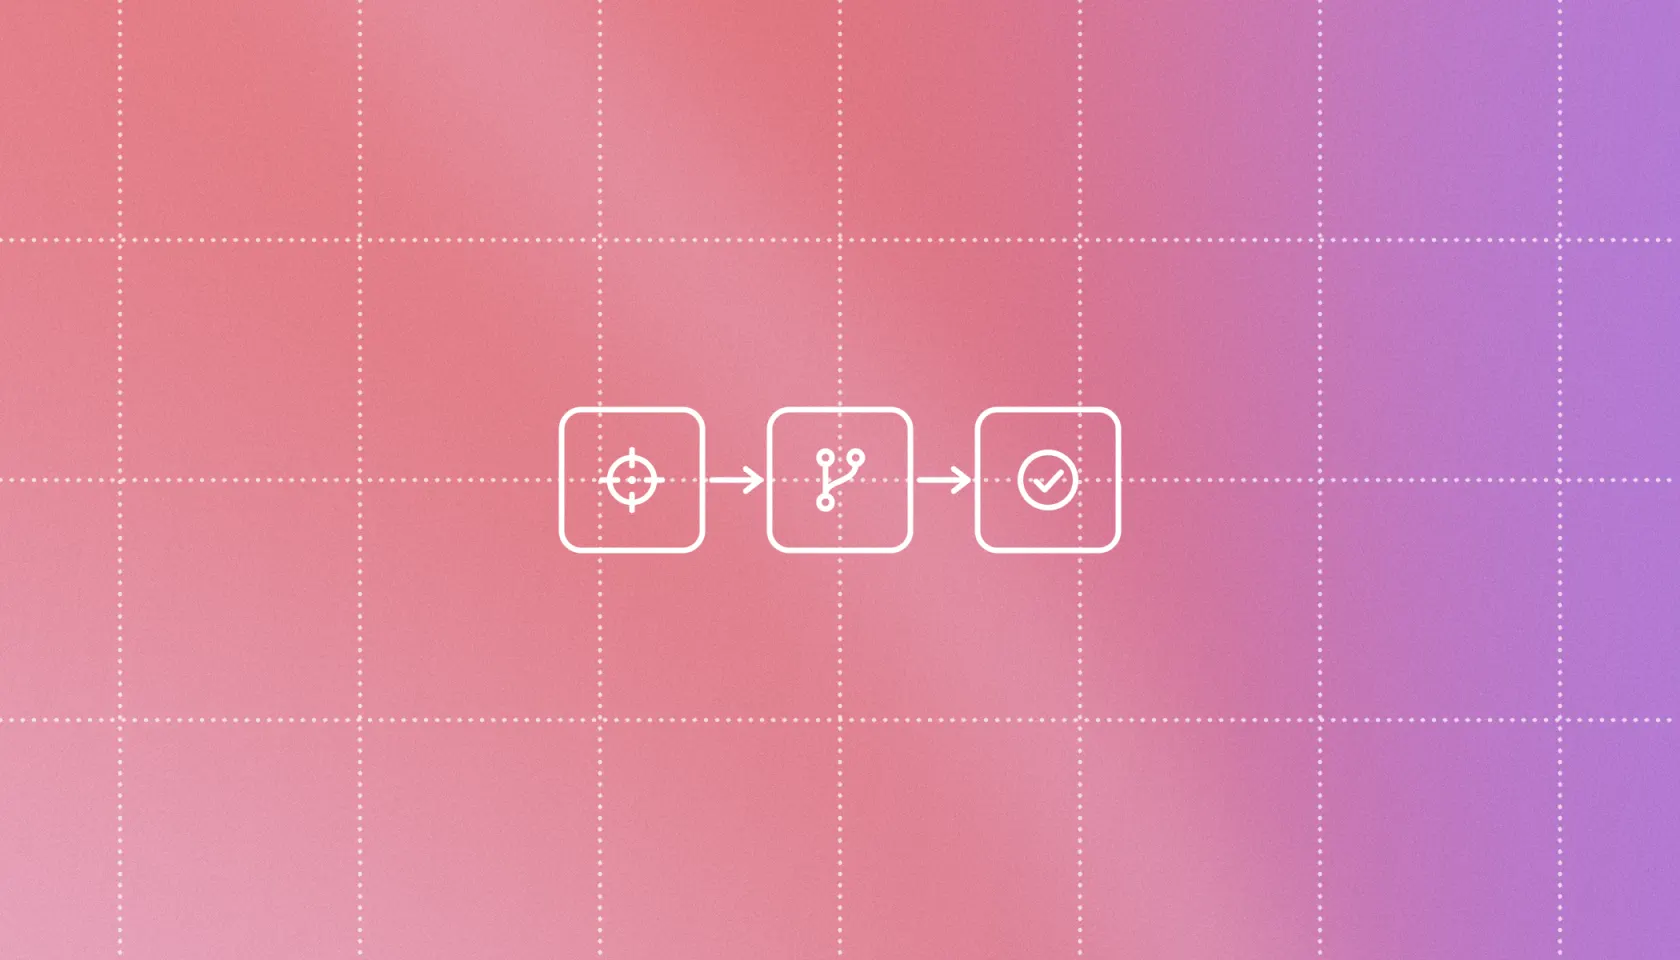
01Alert
Something fires
A SIEM rule, an EDR detection, a cloud or identity event.
02Evidence
Pull the context
Identity, endpoint, network, cloud logs and similar past cases.
03Verdict
Make the call
Real threat or normal business, with the reasoning attached.
04Respond
Act on it
Close it with the evidence, or contain it with an approval.
05Learn
Keep the lesson
Analysts' corrections make the next similar alert faster.
Quick comparison
| Platform | Type | Verdict | Response | Runs | Price |
|---|---|---|---|---|---|
| CloudThinker | Overlay, plus code and app testing | Threat or normal, with evidence | Approved through Auto Mode | SaaS; self-hosted in early access | From $25 a seat, plus credits |
| Dropzone AI | Overlay | Malicious, benign or needs data | IP blocks, account disables | Single-tenant AWS | Quote |
| Prophet | Overlay | Step by step; Inconclusive if unsure | Scoped, automatic or approved | Single-tenant | Per case |
| Torq | Automation platform | Evidence, timeline, summary | Autonomy per agent | SaaS, self-hosted runners | Quote |
| Exaforce | Own data platform, or overlay | False positive, benign or open | Gated by risk or confidence | SaaS in your region | Quote |
| D3 Morpheus | Overlay | Confirmed, inferred or gap | Four autonomy levels | SaaS, on-prem, air-gapped | By alert tier |
| CrowdStrike | Inside Falcon | Verdict with confidence | You choose what runs | SaaS | Credits |
| Microsoft | Inside Defender | Rationale with evidence | Closes false positives | SaaS | $4 per compute unit-hour |
| Google SecOps | Inside SecOps SIEM | Disposition with confidence | Recommends steps | SaaS | Security Tokens |
| Palo Alto Cortex | Inside Cortex | The full attack story | Sensitive actions approved | SaaS in your region | Quote |
1. CloudThinker: an AIOps Control Tower, from code to alert
CloudThinker is our product. We call it the AIOps Control Tower: an AI agent at every post, from the release gate to the alert queue, and your engineers in the tower making the calls. Review checks every code change before it reaches production. Cyber tests running web apps and APIs and reports only what it can reproduce. Resolve for SOC investigates the alerts.
Resolve for SOC takes an alert, checks identity, network, endpoint and cloud logs and similar past cases, and returns a verdict: real threat or normal business, with the evidence and the blast radius. Normal business gets closed with the evidence written down. A real threat comes to your team with a plan. In one fintech customer's production case, an account takeover from an AI phishing attack was contained four minutes after the alert, with one approval. The same customer's 48 GB data-transfer alert turned out to be the nightly backup and closed in two minutes, with nobody paged.
Strengths
- One platform from prevention to investigation: the code review, the app testing and the alert verdicts share the same memory of your systems.
- Verdicts come with the evidence and the blast radius, and benign alerts close with the reason on the record.
- Every change goes through Auto Mode, so you decide what runs on its own and what waits for approval. Commands run in CloudThinker's Sandbox, and secrets become placeholders before any model sees them.
- Published pricing: per seat with a monthly credit pool, from $25 per seat a month on Team, and a Free plan to try it.
Limits
- Newer to the SOC than the specialists below. Documented SIEM and log connections are Splunk, Sumo Logic, Wazuh, Elasticsearch, OpenSearch and Graylog, plus Okta, FortiGate and the major clouds. There's no native EDR connection yet: CrowdStrike, SentinelOne or Defender alerts reach it through a webhook or an MCP server.
- SaaS today. Dedicated and self-hosted deployments are in early access, and there's no FedRAMP authorization.
- The admin audit log is on the Scale plan and up.
Best for teams that want alert investigation tied to the code and cloud they run, and a 14-day replay on their own alerts before they commit. See the AIOps Control Tower for SOC.
2. Dropzone AI: a case file for every alert
Dropzone AI sells an AI SOC Analyst alongside an AI Threat Hunter, generally available since July 2026, and an AI Threat Intel Analyst in beta. It sits on top of your existing stack with no data migration: SIEMs and data lakes such as Splunk, Google SecOps, Elastic and Datadog, EDR from CrowdStrike, Defender and SentinelOne, plus cloud, identity and email tools. Each alert comes back malicious, benign or needs more data, with the evidence, a timeline, the tools it checked and its reasoning. Analysts can correct any verdict.
Strengths
- An overlay with no migration or normalization work.
- A clear three-way verdict, so uncertain alerts are flagged instead of guessed.
- Runs single-tenant on AWS, with in-region deployment for EU customers on request. Its product page lists FedRAMP High authorization; confirm the current status on the FedRAMP Marketplace.
Limits
- The pricing page limits included automated actions to blocking malicious IPs and disabling compromised accounts, on confirmed threats.
- Investigations run under a fair-use cap.
- Pricing by quote, sized on employee count.
Best for teams with an established SIEM and EDR, including public-sector buyers, who want every alert turned into a case file an analyst can review.
3. Prophet Security: an investigation you can read step by step
Prophet AI covers alert triage, threat hunting and, since its July 30, 2026 launch, detection engineering. It plans a fresh investigation for each alert, documents every question, query and reasoning step, and groups related alerts into one incident. When the evidence is thin, it says Inconclusive instead of guessing. It lists more than 200 integrations across SIEM, EDR, identity, email, cloud and data lakes.
Strengths
- A question-by-question audit trail behind every verdict.
- Response through scoped actions that are previewed and backtested against your history before they run, autonomously or with sign-off.
- Optional Watchtower service: human experts review malicious and inconclusive verdicts around the clock.
- Priced per investigation with no data-ingest fees, and a free proof of value with read-only access to two or three sources.
Limits
- No hosting regions documented.
- Detection tuning is listed for Splunk, Sumo Logic and Sentinel only.
- Pricing by quote.
Best for teams that want to read how every verdict was reached, and pay by investigation instead of by data volume.
4. Torq: AI triage on a hyperautomation engine
Torq comes from security automation. Its AI SOC Platform puts agents and an orchestrator called Socrates on top of 300 prebuilt integrations and thousands of workflow steps. In 2026 it raised a $140M Series D, bought Jit for a context graph of identities, privileges and data sensitivity, and announced SOC Brain, which learns from your confirmed verdicts which alerts to automate and which to hand to an analyst.
Strengths
- AI triage and SOAR-style automation in one product.
- Autonomy is set per agent, with role-based access and human-on-the-loop review, and every reasoning step, verdict and action is logged.
- Self-hosted step runners reach VPC and on-prem networks.
Limits
- The site says little about how a verdict is presented to an analyst.
- The value depends on adopting Torq's workflows. SOC Brain's release gave no availability date or pricing.
- Pricing by quote.
Best for large SOCs replacing a SOAR that want triage and automation from one vendor.
5. Exaforce: fine-grained approval gates
Exaforce runs four agents it calls Exabots (Detect, Triage, Investigate and Respond) on its own data platform, which it positions as a SIEM replacement. It can still query Splunk, Sentinel, Elastic, Google SecOps or Cortex XSIAM. Triage returns false positive, benign or needs investigation, with a plain-English rationale, key indicators and links to the evidence. It raised a $125M Series B in May 2026.
Strengths
- The most detailed response gates we found: by action sensitivity, user risk, confidence or business hours, approved in Slack, Teams or email, with a safe default when an approval times out.
- Named actions include isolating cloud instances, quarantining email, resetting MFA and revoking sessions.
- SaaS in the region you choose, or bought as a managed service.
Limits
- Real-time analysis covers the last 90 days held in memory. Older data stays in your SIEM.
- Exaforce says edge cases may need an external SOAR, and you get the most from it when your data moves into its platform.
- Pricing by quote.
Best for cloud- and SaaS-heavy teams open to replacing a legacy SIEM, who want fine control over automated response.
6. D3 Morpheus: named autonomy levels, including air-gapped
D3 Morpheus traces each alert across identity, endpoint, cloud and email, and grades every finding Confirmed, Inferred or Gap. When it's uncertain, it defers to a human. D3 lists more than 800 connectors and says they repair themselves when a vendor's API changes.
Strengths
- Four autonomy levels: Deterministic (no AI in the response chain), AI-Assisted, AI-Led and Autonomous.
- SaaS in several regions, or on-prem and air-gapped with AI inference kept inside your boundary, and you can bring your own model.
- A published pricing model: an annual subscription by daily alert tier, from 500 to 10,000 alerts a day, with no billing for model tokens.
Limits
- D3 says peak accuracy takes 60 to 90 days to reach.
- Threat Hunting is planned for the end of November 2026, and Attack Path Discovery 2.0 was still in pilot in June.
- Dollar prices by quote.
Best for regulated teams and MSSPs that need explicit autonomy levels or an air-gapped deployment.
7. CrowdStrike Charlotte AI: agents inside Falcon
Charlotte AI runs agents across endpoint, identity, cloud and network data in the Falcon platform, with shared memory. The triage agent returns a verdict, a confidence score, a recommendation and its reasoning, traced to the data behind it. Charlotte Agentic SOAR adds workflows with an autonomy level per workflow and MCP in both directions. In 2026 CrowdStrike launched the AgentWorks ecosystem for building agents and made an MCP server for third-party agents generally available.
Strengths
- Confidence-scored verdicts, traced to Falcon data.
- No automated actions by default: you choose what runs on its own and what needs approval.
- Qualifying Falcon customers get Charlotte AI with 50 AI credits a month at no extra cost, and Agentic SOAR has a 15-day free trial.
Limits
- Built for data in Falcon.
- At Fal.Con 2026, some agentic investigation features were pre-beta or in public preview.
- The Essentials tier of Agentic SOAR leaves out the triage and response agents. Credit pricing by quote.
Best for Falcon customers who want governed agents without adding a vendor.
8. Microsoft Security Copilot: triage agents for Defender shops
Security Copilot agents work across Defender XDR, Sentinel, Entra, Intune and Purview. The Security Alert Triage Agent grew out of the phishing triage agent: email and phishing alerts are generally available, and some identity alerts (password spray, suspicious inbox rules) and some cloud and container alerts are in preview. It shows its rationale, the evidence it used and a visual of its reasoning.
Strengths
- The only list price on this page: $4 per provisioned compute unit per hour, $6 for overage. Microsoft 365 E5 includes 400 compute units a month for every 1,000 user licenses, up to 10,000.
- It resolves false positives and leaves true positives open for an analyst.
- An analyst approves feedback before it enters the agent's memory.
Limits
- It triages Defender-generated alerts, and each alert type needs its matching Defender or Entra license.
- Identity and cloud triage are in preview, and teaching the agent through feedback works for email alerts only.
- Containment actions by the agent aren't described.
Best for Microsoft 365 E5 and Defender shops starting with phishing triage.
9. Google Security Operations: confidence-scored triage in the SIEM
Google SecOps' Triage and Investigation agent went generally available in June 2026. It works on alerts in Google SecOps SIEM, uses dynamic search, Google Threat Intelligence, command-line analysis and process trees, and returns a true or false positive with a confidence level, a summary of how it decided, and next steps. A run takes about 60 seconds on average. Google says the agent has investigated more than 5 million alerts (vendor claim). Threat hunting and detection engineering agents are in preview.
Strengths
- A confidence level on every disposition.
- Google's threat intelligence built into the investigation.
- Fast runs, with a 20-minute maximum.
Limits
- SIEM data only: it doesn't process alerts from the SecOps SOAR connector, and there's no investigation queue.
- It recommends next steps. It doesn't take automated actions.
- Its docs say it isn't FedRAMP compliant. It's metered by Security Tokens: Enterprise Plus contracts get a daily allotment, and the Enterprise tier doesn't.
Best for Google SecOps SIEM customers, ideally on Enterprise Plus.
10. Palo Alto Networks Cortex: agents across XSIAM and AgentiX
Cortex XSIAM groups alerts into cases that show the full attack story, and Cortex AgentiX, the successor to XSOAR, adds agents with more than 1,100 prebuilt integrations and native MCP. Agents run commands, playbooks and scripts with the permissions of the analyst who invoked them. Actions marked sensitive need manual approval, and every action is logged. Palo Alto bought Console in September 2026 to deepen these agentic features.
Strengths
- The largest integration library on this list.
- Agents inherit the analyst's permissions, and sensitive actions wait for approval.
- A SaaS tenant in the region you choose.
Limits
- The agentic assistant is available in a listed set of regions only, not on the MSSP main tenant, and only EU and US tenants can choose the model.
- Built for buyers consolidating on Cortex.
- Pricing by quote.
Best for enterprises consolidating SIEM, XDR and SOAR on Palo Alto Networks.
Also worth a look
Intezer pairs AI with deterministic forensics (sandboxing, reverse engineering, memory analysis) and prices by endpoint, which suits endpoint- and phishing-heavy teams. Splunk Enterprise Security has triage and response agents inside the SIEM, but they need the Premier edition plus a paired SOAR, with a cap of about 200 findings per tenant a day. SentinelOne Purple AI opened its agentic investigation to all customers in June 2026, metered by Singularity Credits. 7AI covers the whole SOC with agents plus dedicated engineers, Conifers puts a confidence score on every verdict and can run inside your own Azure tenant, and Qevlar runs the same investigation for the same alert every time, hosted in the EU.
Radiant Security, a regular in older roundups, is a different story now: Cribl bought its AI SOC technology in August 2026 and is rebuilding it into its own platform.
How to choose
Start with where your alerts live. If you're all in on Falcon, Defender, Google SecOps or Cortex, the built-in agent is the cheapest first step, but it mostly sees that platform's data. If your alerts come from a mix of tools, an overlay like Dropzone, Prophet, D3 or CloudThinker fits better.
Read a verdict, not an accuracy number. Every vendor publishes a high one, measured its own way. Ask for a real case file instead: what the agent checked, what it ruled out, and what it says when it isn't sure. Prophet and Qevlar answer Inconclusive. Dropzone says it needs more data. D3 grades each finding Confirmed, Inferred or Gap.
Decide who presses the button. Response ranges from recommendations only (Google) to gated autonomous actions (Exaforce, D3). Ask how an approval works at 3 a.m.: where it shows up, who can approve, and what happens if nobody does.
Check deployment early. If your data can't leave your network, the list gets short fast: D3 runs on-prem and air-gapped, Torq has self-hosted runners, and CloudThinker's self-hosted deployment is in early access. If you need EU hosting, Dropzone deploys in-region on request and Qevlar is hosted in the EU.
Price your real volume. Per investigation, per employee, per endpoint, per alert tier, per credit, per compute unit: the models don't compare on a slide. Take last month's alert count and ask each vendor for a quote against it.
Replay before you buy. Give each finalist read-only access and two weeks of recent alerts. Compare its verdicts with what your analysts decided, and read the cases where they disagree.
Getting started
Connect your SIEM read-only, pick a week of alerts your team has already closed, and ask:
"Investigate this alert: is it a real threat or normal business? Show me the evidence you checked."
"Replay last week's high-severity alerts and tell me which ones you'd have closed, and why."
Start with a 14-day replay on your own alerts through the AIOps Control Tower for SOC.
Questions people ask
What is an AI SOC platform?
An AI SOC platform uses AI agents to do the investigation work of a security operations center. The agent takes an alert from your SIEM, EDR, identity or cloud tools, pulls the evidence it needs, and returns a verdict: a real threat or normal business, with the reasoning attached. Most platforms can also take or propose a response, such as revoking a session or blocking an IP, under approval rules you set.
What are the best AI SOC platforms in 2026?
As of November 2026, the platforms most often evaluated are CloudThinker, Dropzone AI, Prophet Security, Torq, Exaforce and D3 Morpheus as standalone products, and CrowdStrike Charlotte AI, Microsoft Security Copilot, Google Security Operations and Palo Alto Networks Cortex as agents built into a larger platform. Intezer, Splunk Enterprise Security, SentinelOne Purple AI, 7AI, Conifers and Qevlar are also worth a look. The right pick depends on where your alerts live, how much autonomy you'll allow, and where the platform has to run.
What is the difference between an AI SOC platform and SOAR?
SOAR runs playbooks that someone wrote in advance, step by step. An AI SOC agent decides what to check for each alert, follows the evidence, and explains its verdict, so it handles alerts no playbook anticipated. Many teams keep SOAR for the response actions and put the AI agent in front of it for investigation. Some vendors, such as Torq and Palo Alto Networks' Cortex AgentiX, sell both in one product.
Does an AI SOC platform replace a SIEM?
Usually not. Most AI SOC platforms sit on top of the SIEM and EDR you already run and query them during an investigation. A few, such as Exaforce, offer their own data platform and position it as a SIEM replacement. The platform-built agents from Google, Microsoft, CrowdStrike and Palo Alto Networks work best, or only, on data inside their own platform.
How do AI SOC platforms take action safely?
Through approval rules you set. The common pattern is that the agent closes false positives on its own, and anything that changes a system, such as disabling an account or isolating a host, waits for an analyst's approval until the team trusts that action class. Exaforce gates actions by sensitivity, user risk or confidence. D3 Morpheus names four autonomy levels. CloudThinker sends every change through Auto Mode, where you decide what runs on its own and what waits for approval.
How are AI SOC platforms priced?
Every way you can think of. Prophet prices per investigation, Dropzone by employee count, Intezer by endpoint, and D3 Morpheus by daily alert tier. CrowdStrike, Google, SentinelOne and CloudThinker use credits or tokens. Microsoft Security Copilot is the only one with a list price per compute unit, and Microsoft 365 E5 includes a monthly allotment. Most standalone vendors quote, so price your real alert volume, not a demo.